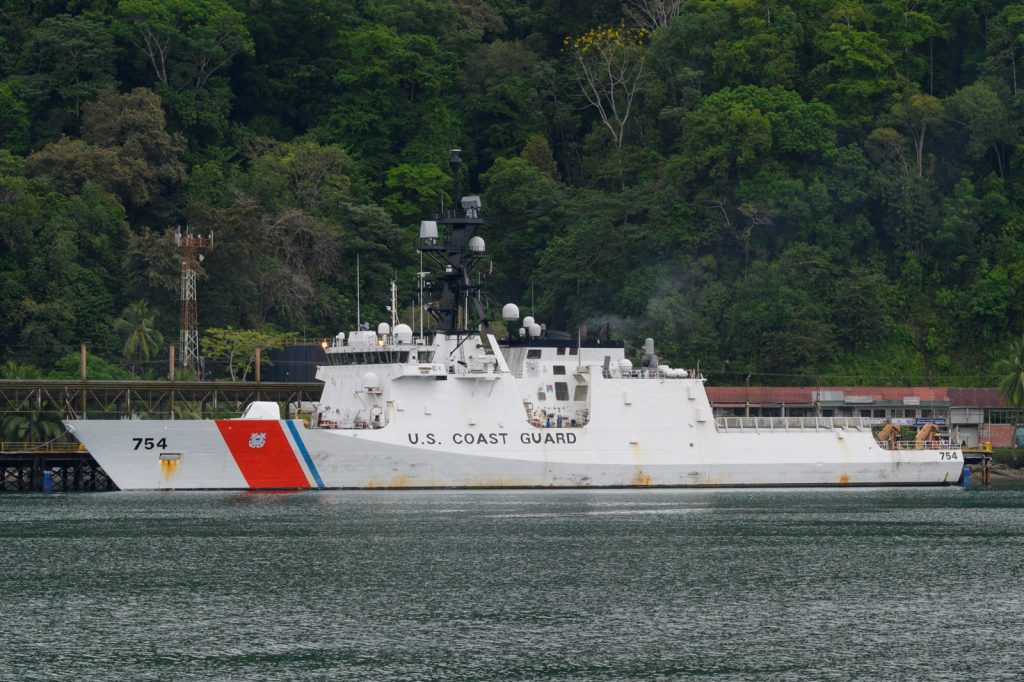
The tanker VL Prosperity sat at anchor off Galveston, Texas, while a team of Coast Guard law-enforcement personnel, a vessel inspector, Coast Guard Cyber Protection Team members and FBI cyber specialists went aboard. The first inspection reportedly took place on August 21, with a second a few days later. The ship had come in under suspicion that someone had broken into its networks.
On September 16 the FBI and the Coast Guard confirmed the investigation in a joint statement to The Wall Street Journal. They said the inspections were meant to check the integrity of the vessels’ operational and information technology systems after signs that the networks of both ships had been compromised by foreign actors. The statement added that there were no reports of operational disruptions, vessel instability, physical danger to crews or environmental impacts.
Iranian media got there first
Officials gave no details, but suspicion landed on Iran quickly. Iranian outlets had been reporting trouble since early August. Tasnim, which is reported to be linked to the Islamic Revolutionary Guard Corps, ran a story on August 20 saying VL Prosperity was hit by a major cyberattack in the Strait of Gibraltar and lost all communications for 30 hours. Citing a crew member, it claimed the attackers got into engine-room systems, cut the engine’s cooling flow and raised its speed. Mehr News Agency carried similar claims. Tasnim followed up with a piece headlined “No American Vessel is Safe Anymore.”
The Liberian-flagged tanker, managed by HMM Ocean Services, was bound for Galveston. HMM confirmed to CBS News that its vessel was under investigation. A second ship, an LNG carrier, was also reported to have alerted the authorities. Cybernews later named the two Texas-bound vessels as VL Prosperity and Kokahu, and said Coast Guard and FBI teams were sent to help in late August.
A third ship, and unproven claims
The picture grew more tense days later. Cybernews reported on September 21 that the crew of Vivit Africa, a Liberian-flagged LNG tanker built in 2023, said attackers briefly took hold of safety-critical systems. The ship left Louisiana on August 20 and was due to unload at the Adriatic LNG terminal near Rovigo, Italy, on September 7. It aborted the discharge, was diverted to Barcelona, and reported the failures to the Korean Register and the Italian Coast Guard.
In an email to the shipping publication Splash247, the crew wrote that the vessel “was targeted by cyber attackers prior to berthing at this terminal.” They claimed the intruders reached tank pressure control systems and pressure relief valves and disrupted the boil-off gas cycle, which they said raised “the risk of tank rupture and explosion.” Neither authority has publicly confirmed an attack on that ship. The Italian Coast Guard reportedly spoke only of a malfunction in systems that monitor cargo parameters, which needed company technicians to fix.
All three ships were passing through the Strait of Gibraltar when their systems failed.
The Department of Homeland Security has confirmed that the United States is watching at least 20 other commercial fuel tankers at sea while the FBI looks into possible ties to Iran-linked hackers. The Coast Guard has asked any vessel approaching U.S. ports to notify its maritime security branch before entering.
Gabrielle Hempel, a security strategist at Exabeam who also leads cybersecurity education for the Coast Guard, told Cybernews that an attacker does not need full control of a tanker to create danger. Disrupting the right subsystem at the wrong moment can be enough.
Sources
- USCG and FBI Investigate Cyberattacks on US-Bound Tankers
- Third tanker hack: crew claims attackers took control | Cybernews